Business sites, media and WooCommerce stores
Has your WordPress site changed? You know at the first sign
Most WordPress vulnerabilities are in plugins, and they are often exploited within hours of being published. Whether your site showcases your business, publishes your content or sells online, Tocsin24 monitors its core, plugins and themes, its uptime, and its sales if it runs WooCommerce.

Designed by a developer who has been looking after websites and online stores for 18 years.
Integrity of the core, plugins and themes
The core, plugins and themes are compared with their state when first checked; recognised updates do not trigger an alert.
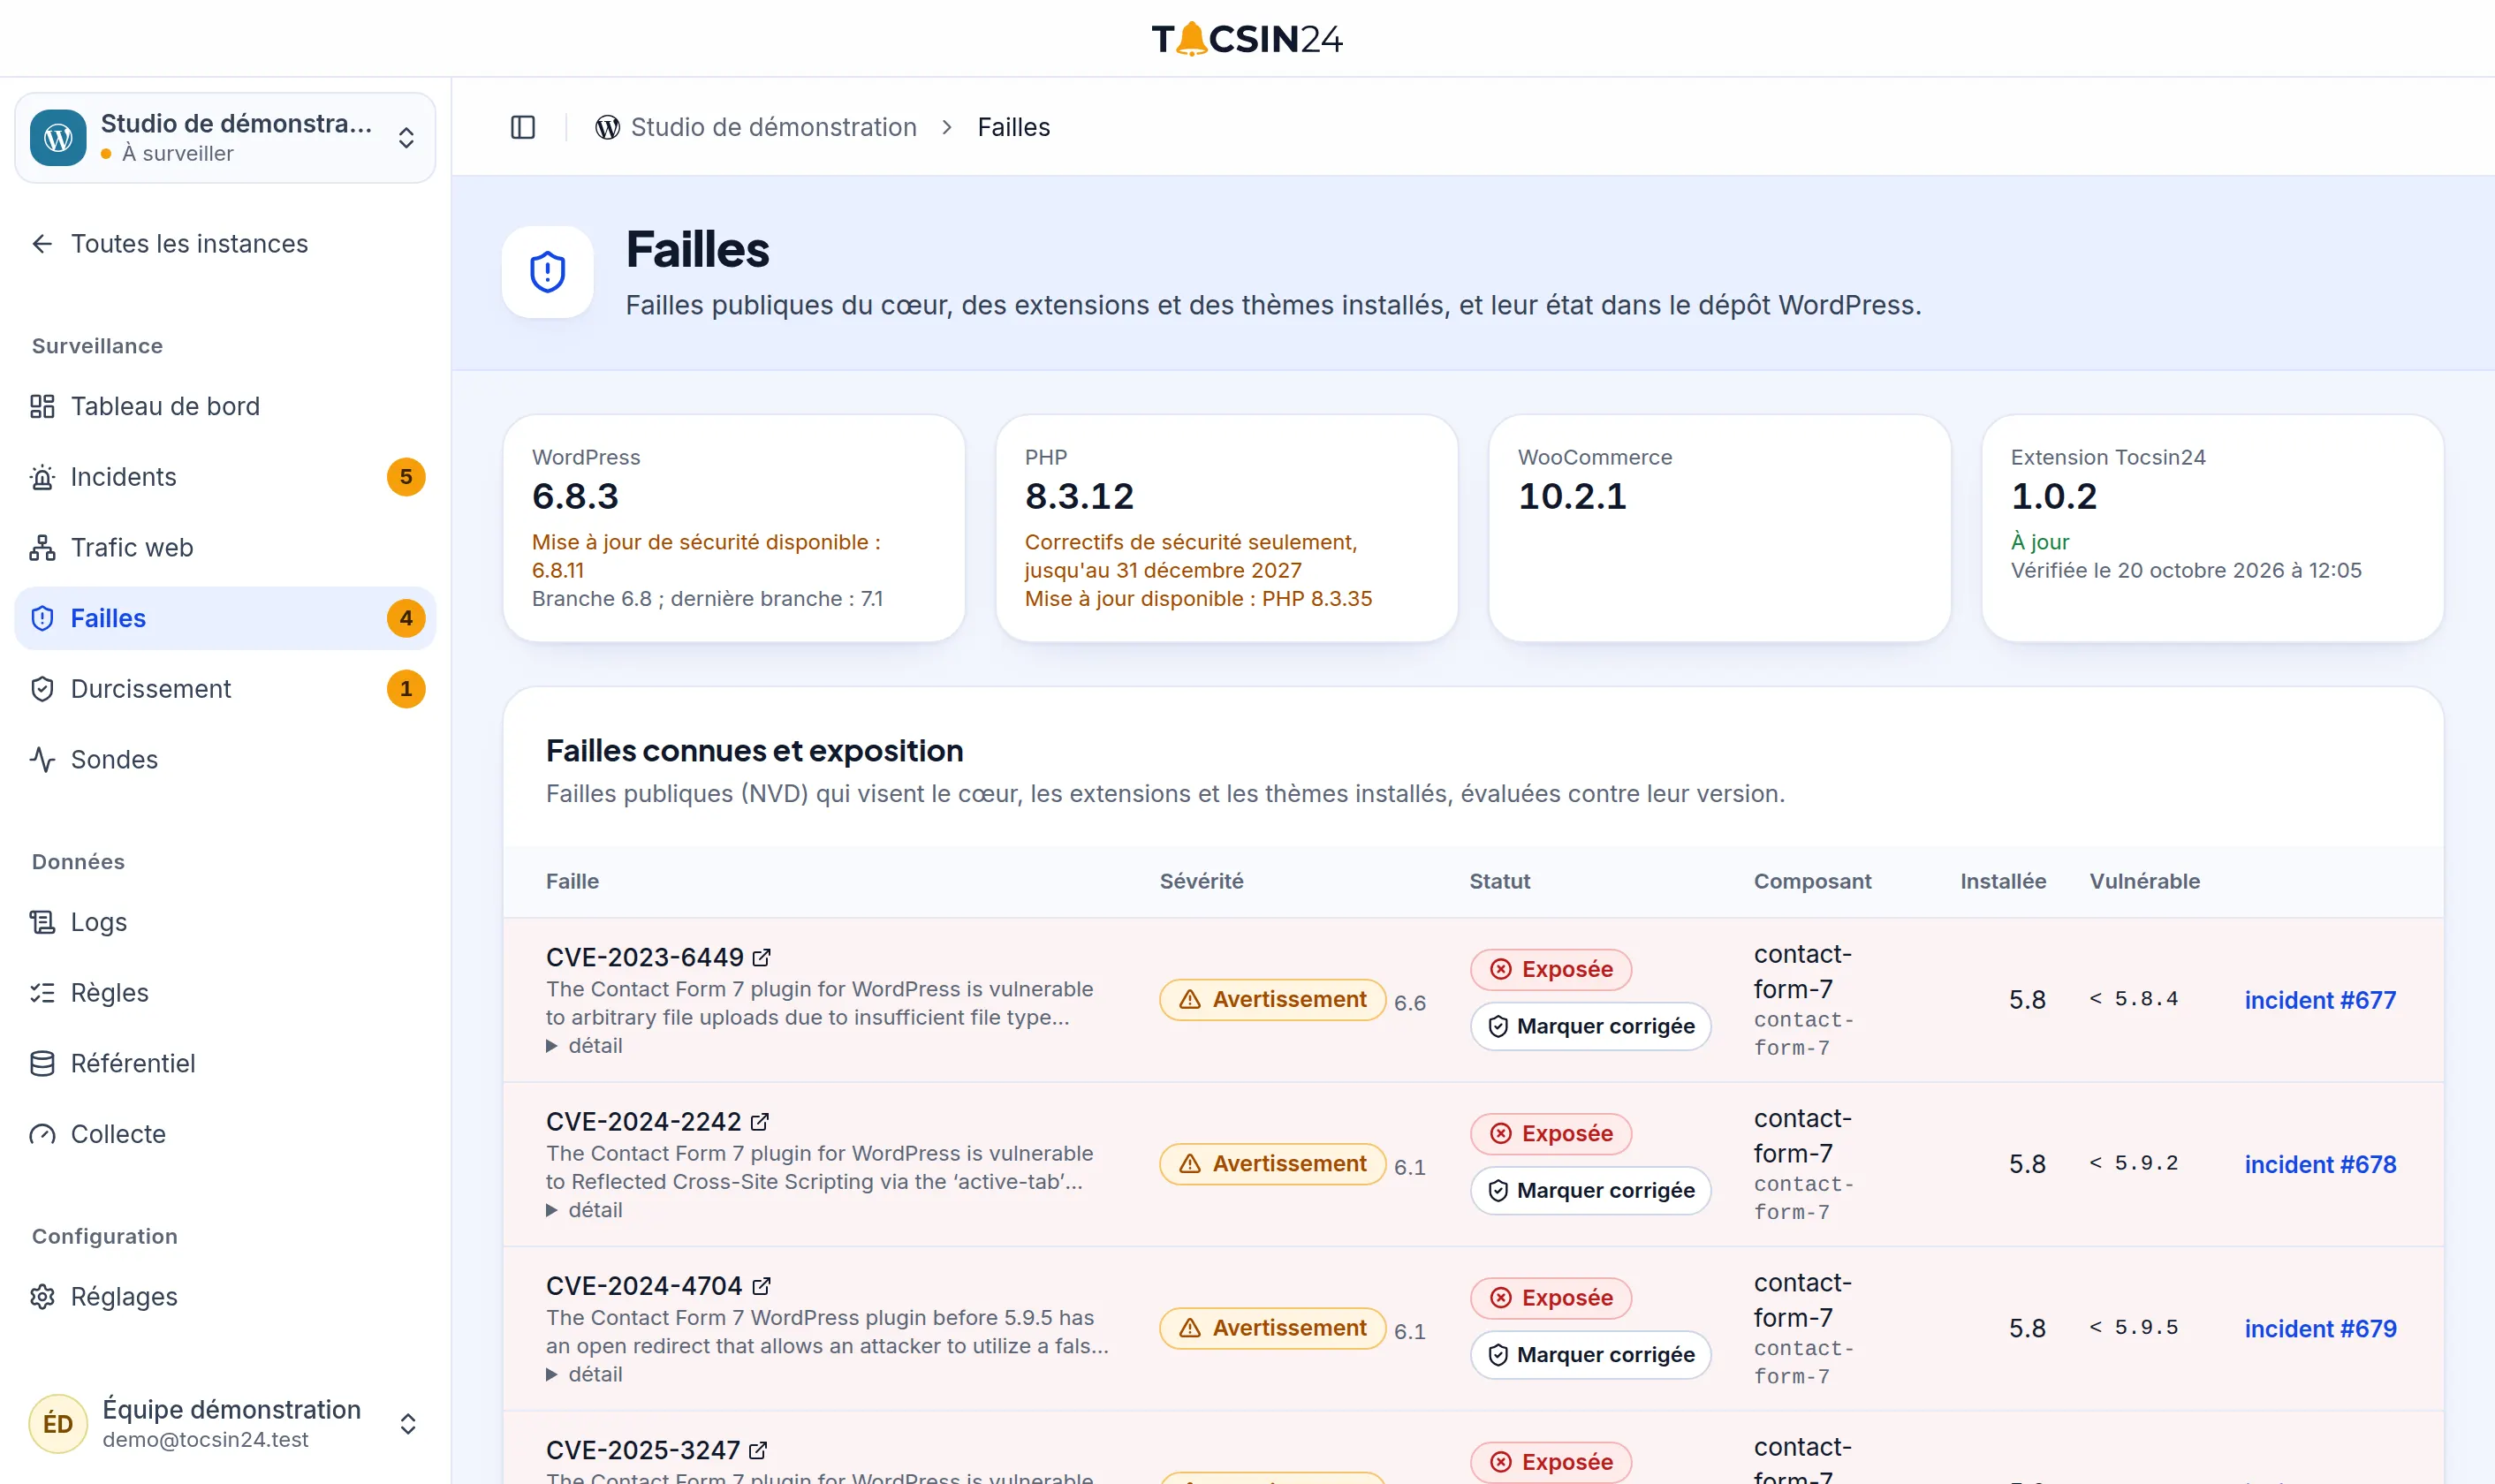
Known vulnerabilities
Known vulnerabilities in your installed plugins and themes, and plugins that have been removed from or abandoned on the WordPress directory.
New administrator accounts
Every new administrator account and every unexpected file in the media library is reported.
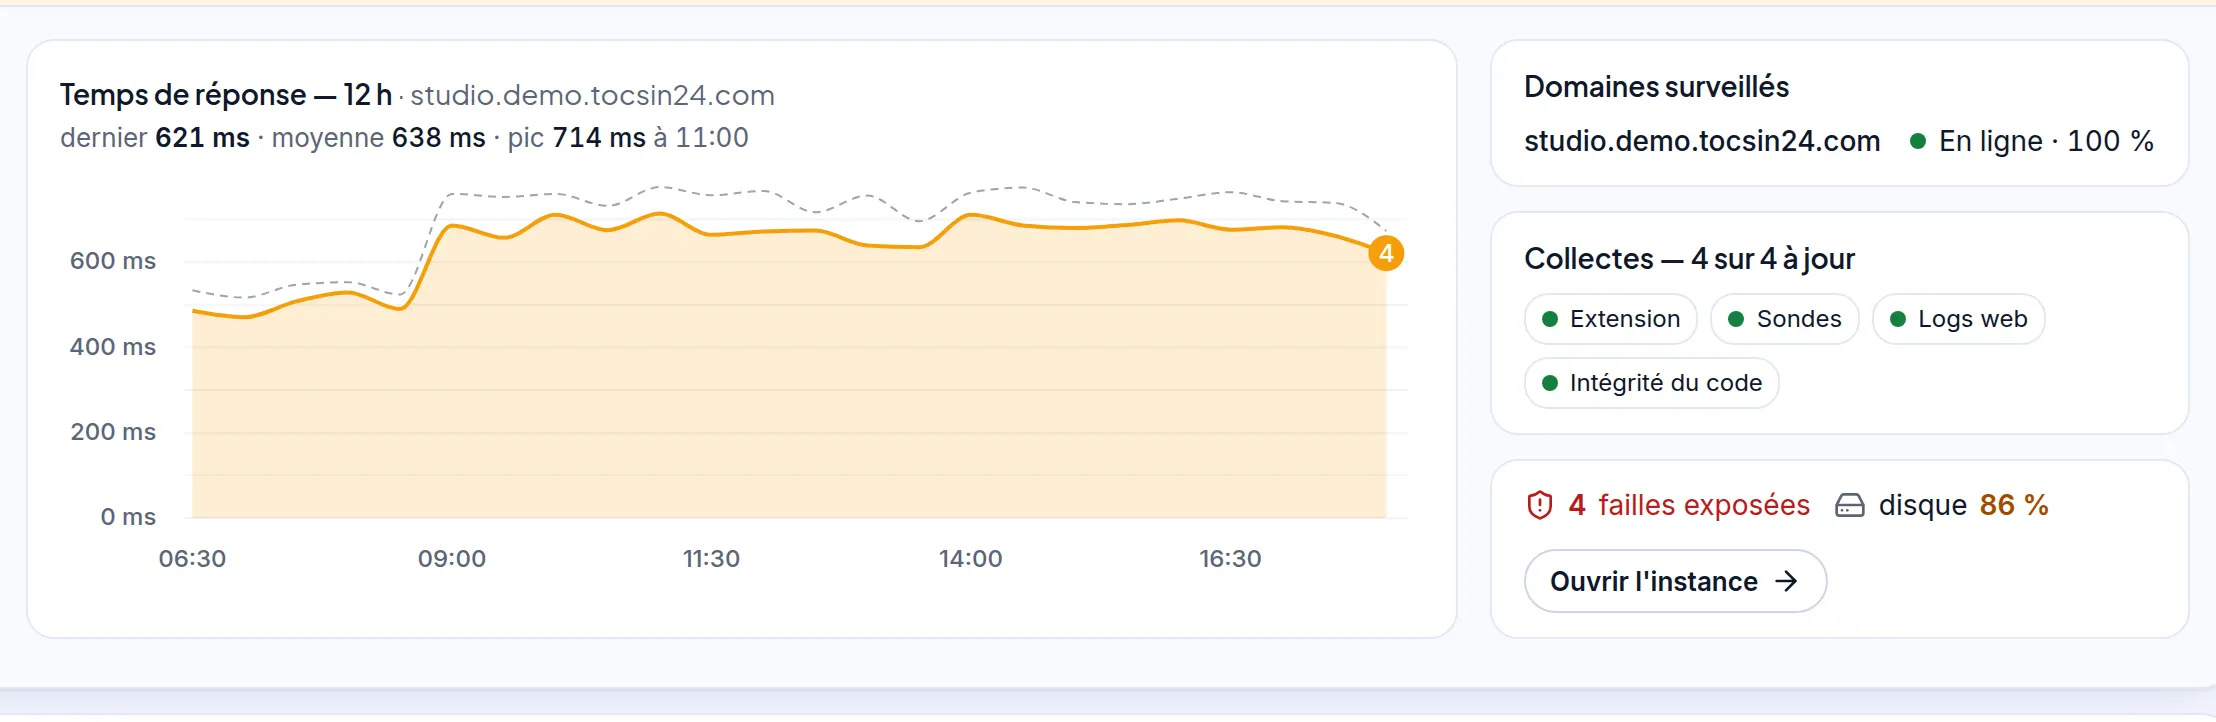
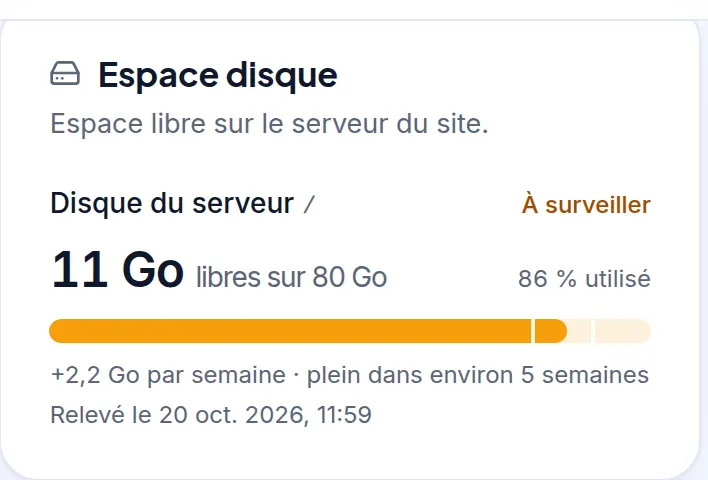
Uptime, response time and disk space
WooCommerce sales stores
Orders and sign-ups, with unusual dips reported.
Alongside your security plugin
Tocsin24 does not block anything; it monitors and explains, alongside your firewall.
€19 excl. VAT per month, per site or €190 excl. VAT per year
- Staging sites at half price
- Assisted setup from €149 excl. VAT
Questions
I already use Wordfence (or another security plugin): is this still useful?
Yes, as a complement: your plugin blocks, while Tocsin24 checks what has changed on your site, compares it with its state when first checked and explains what to do.
My site is not an online store: is it for me?
Yes. Sales monitoring only applies to WooCommerce stores; everything else (security, uptime, alerts) works for any WordPress site.
Does the plugin slow the site down?
No. The plugin does not run while pages are being displayed: it answers the platform’s checks and runs its code check once an hour, in the background, without re-reading unchanged files. On a very busy site, we recommend handing WP-Cron over to the server’s cron.