Magento Open Source and Adobe Commerce
Magento store monitoring, by a Magento developer
Magento vulnerabilities are exploited within hours, while patches often take weeks to be applied. Tocsin24 tells you at the first sign whether your store is exposed, has been tampered with or has gone down.

Checks designed by Cédric Michel, a Magento developer for 18 years and an Adobe Commerce Developer Expert (see the certification).
Adobe patches checked inside the store
Tocsin24 reads the patches declared in the store and checks their files: if a patch has been removed, you are told. The status is never guessed from the version number.
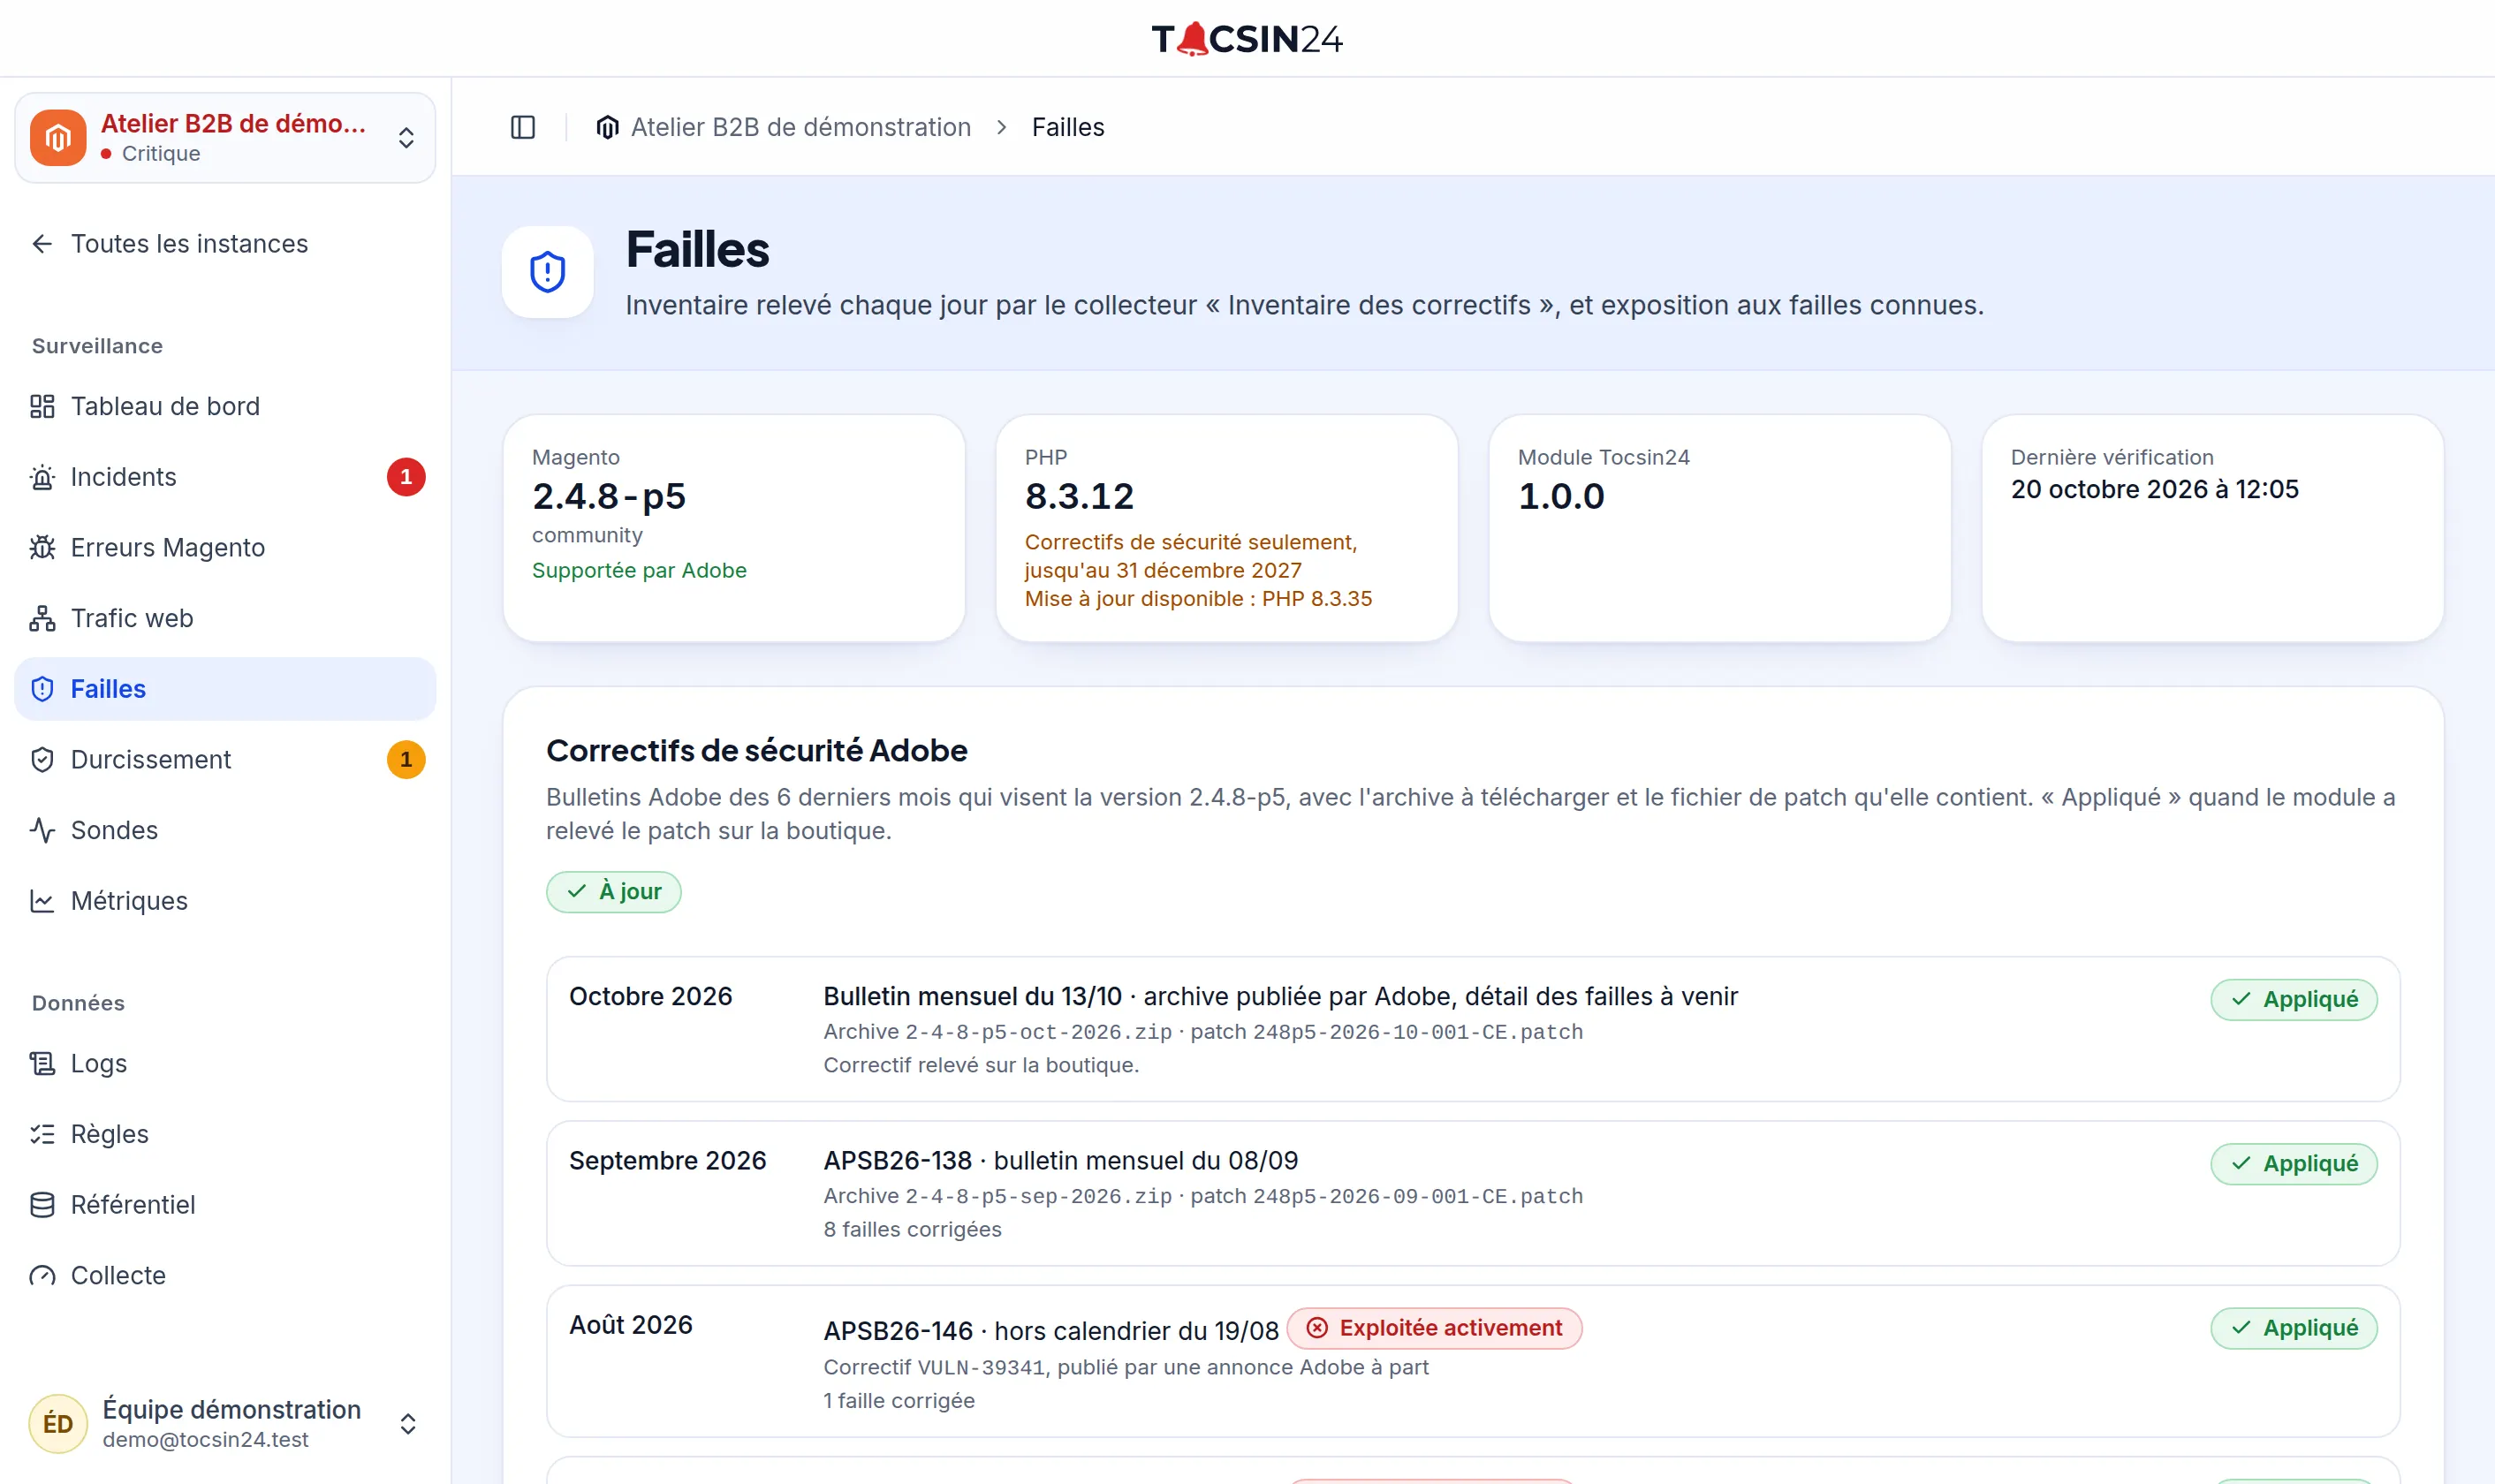
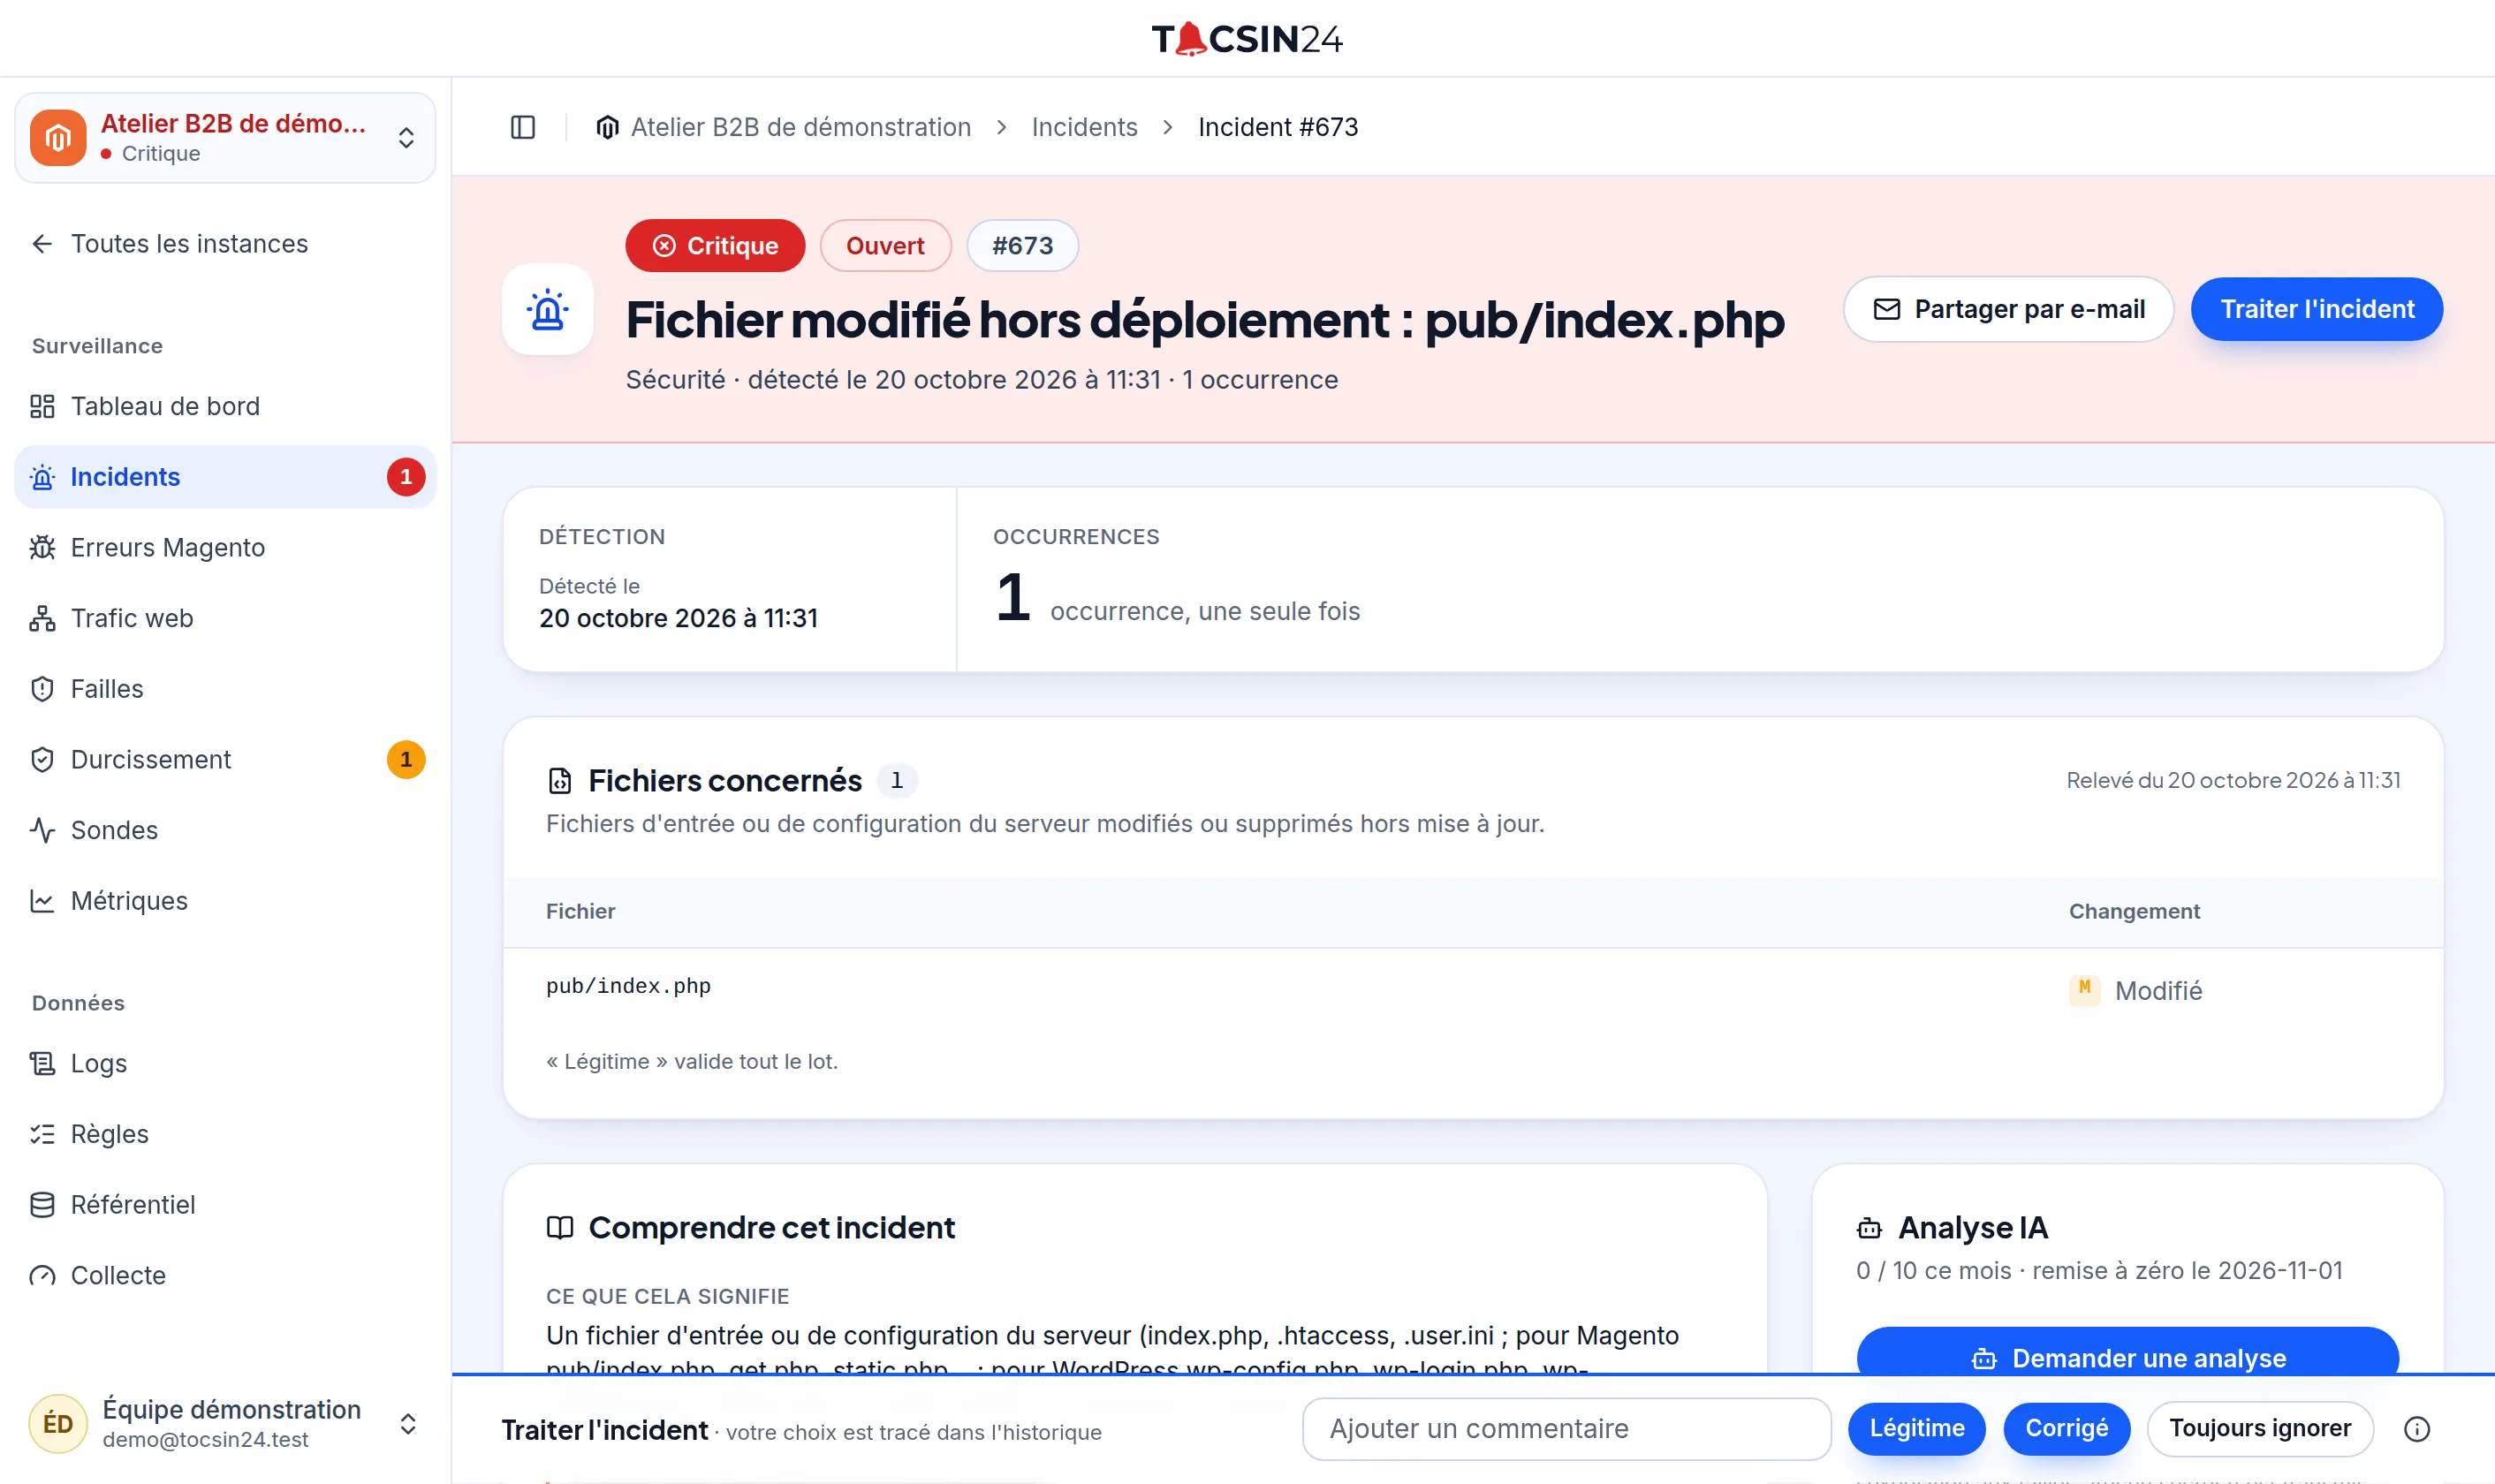
Code integrity
Any core or extension file changed outside a deployment is reported. The most sensitive files (entry points, payment, customer accounts) are also compared with the official files of your version, from Magento 2.4.4 onwards. A file changed outside a deployment triggers a critical alert, with the command to compare it with the original.
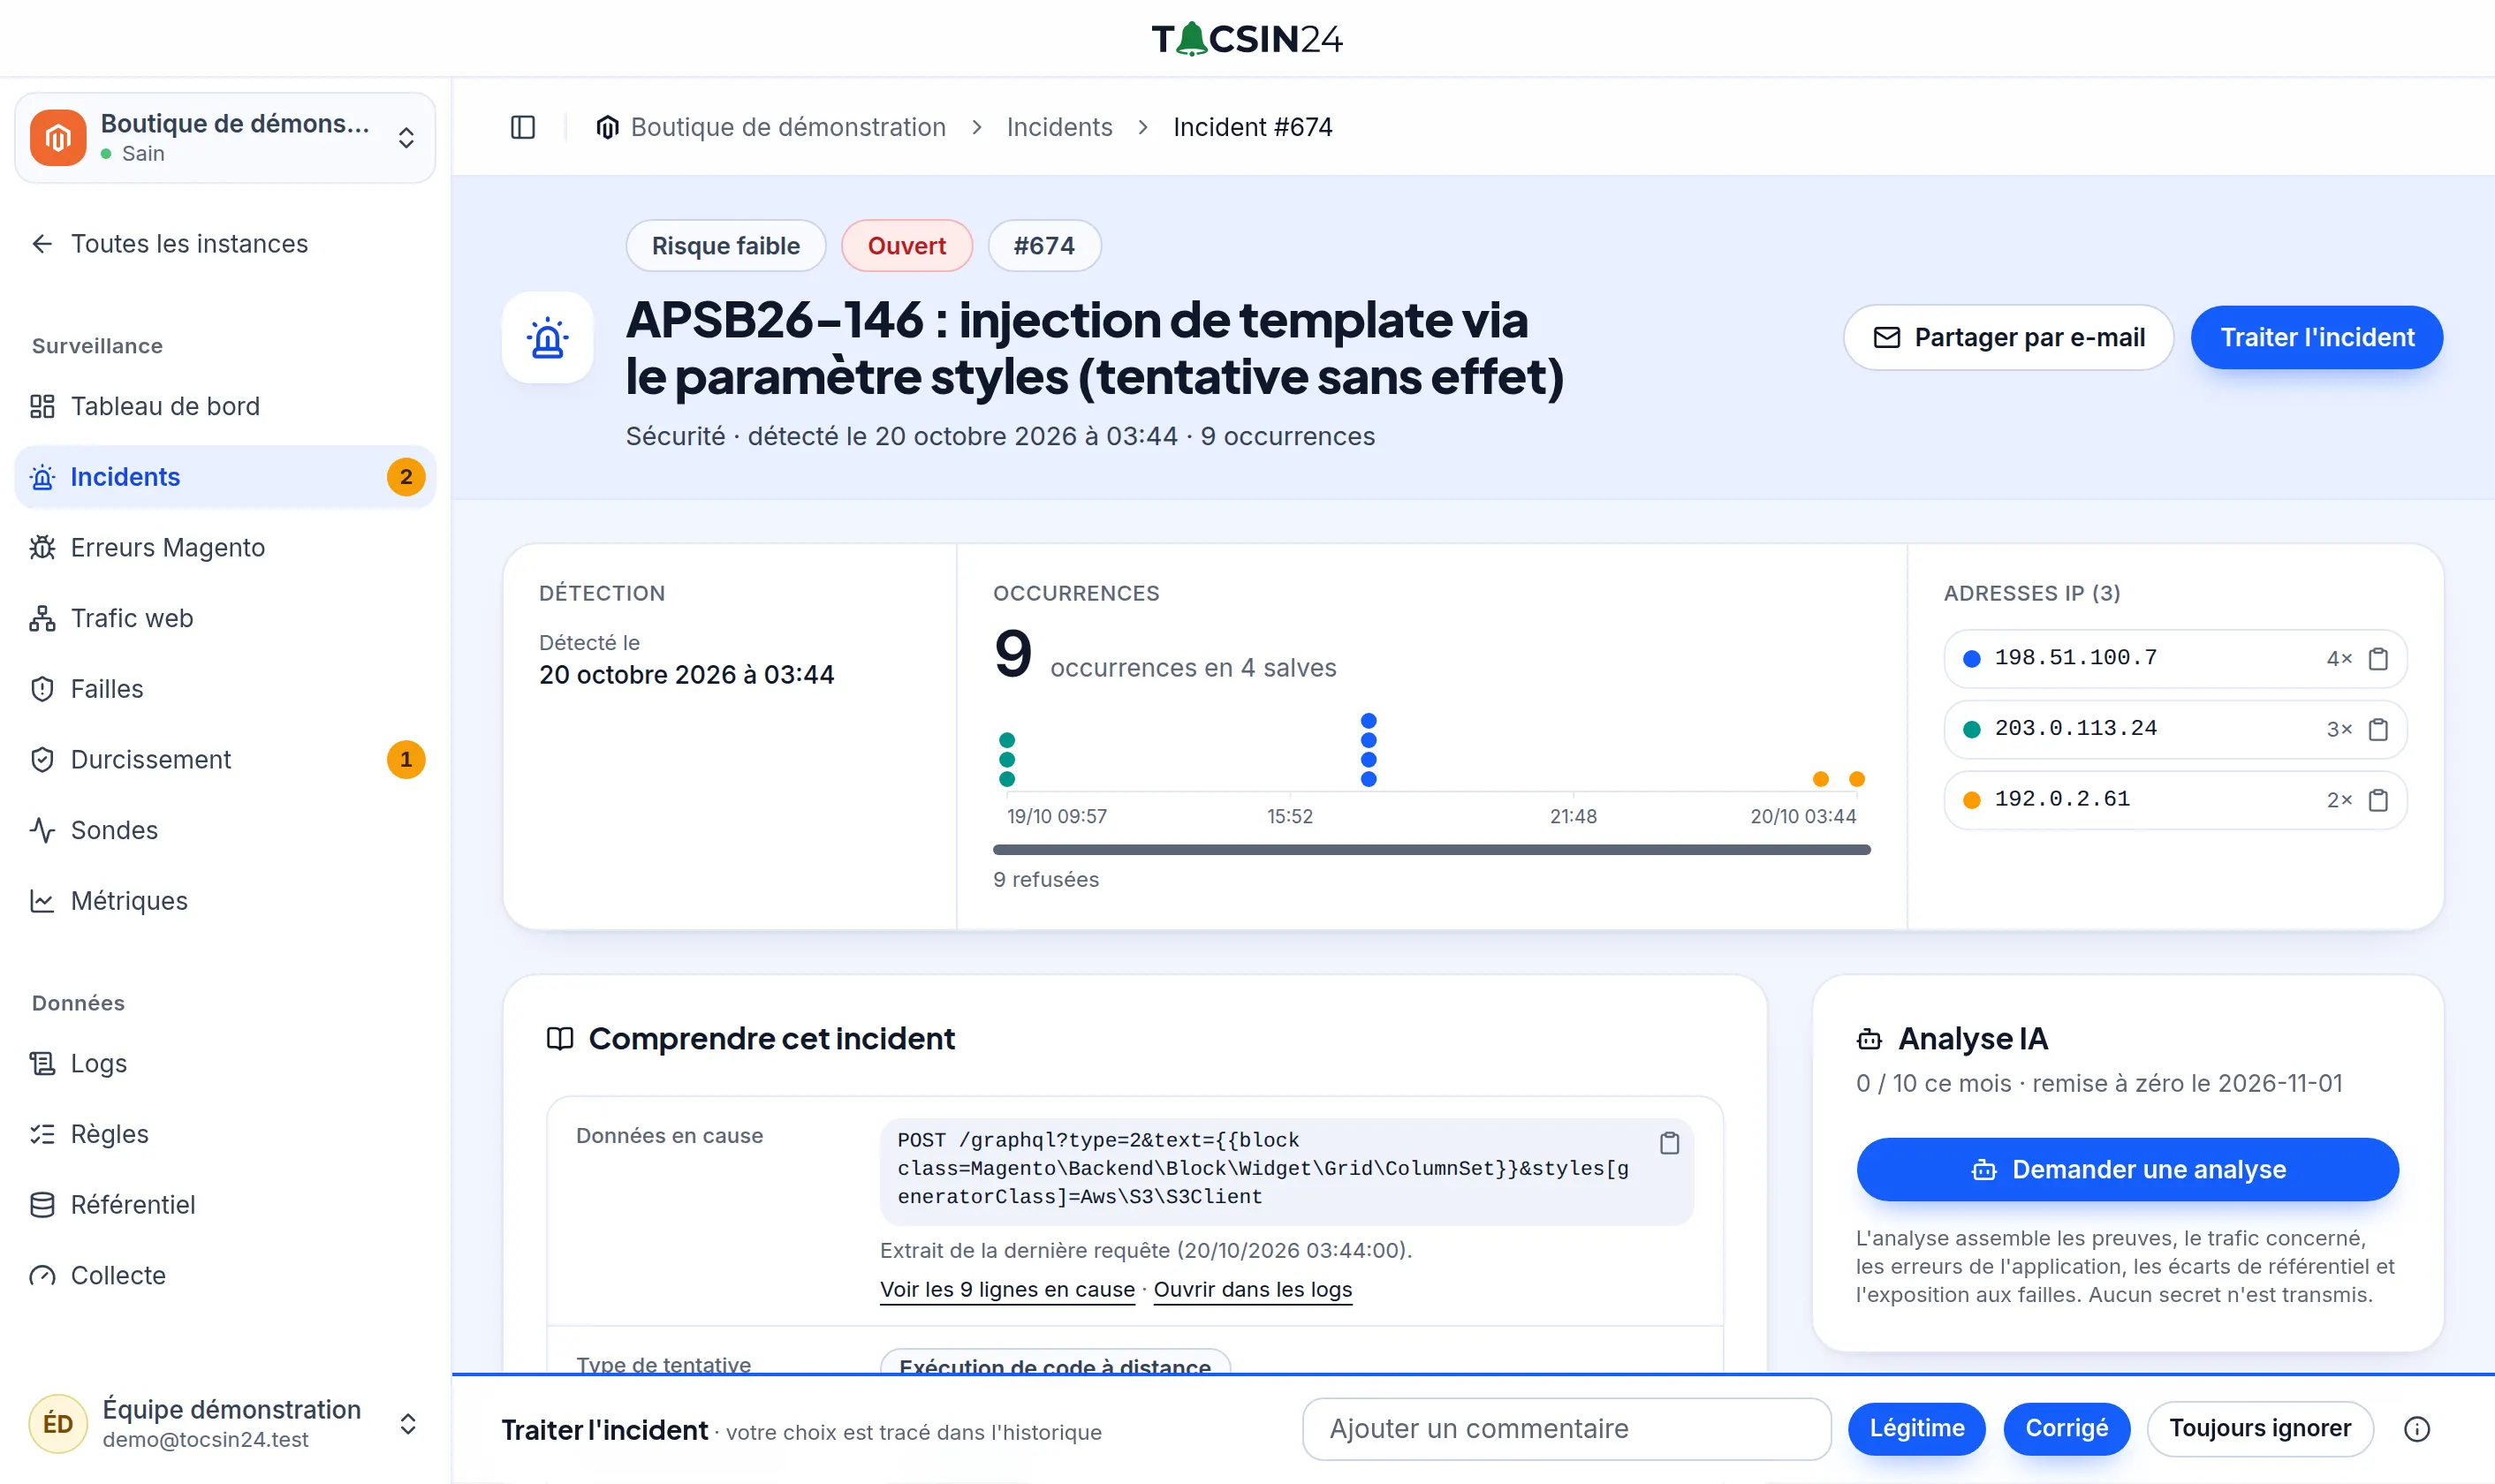
Exposure to known vulnerabilities
Installed versions and extensions, matched against published vulnerabilities and whether they are being actively exploited.
Accounts, integrations, API tokens, CMS blocks
Anything unexpected that appears is reported.
Signs of attack in the logs
Attempts are recognised along with their outcome: blocked, uncertain or needing action.
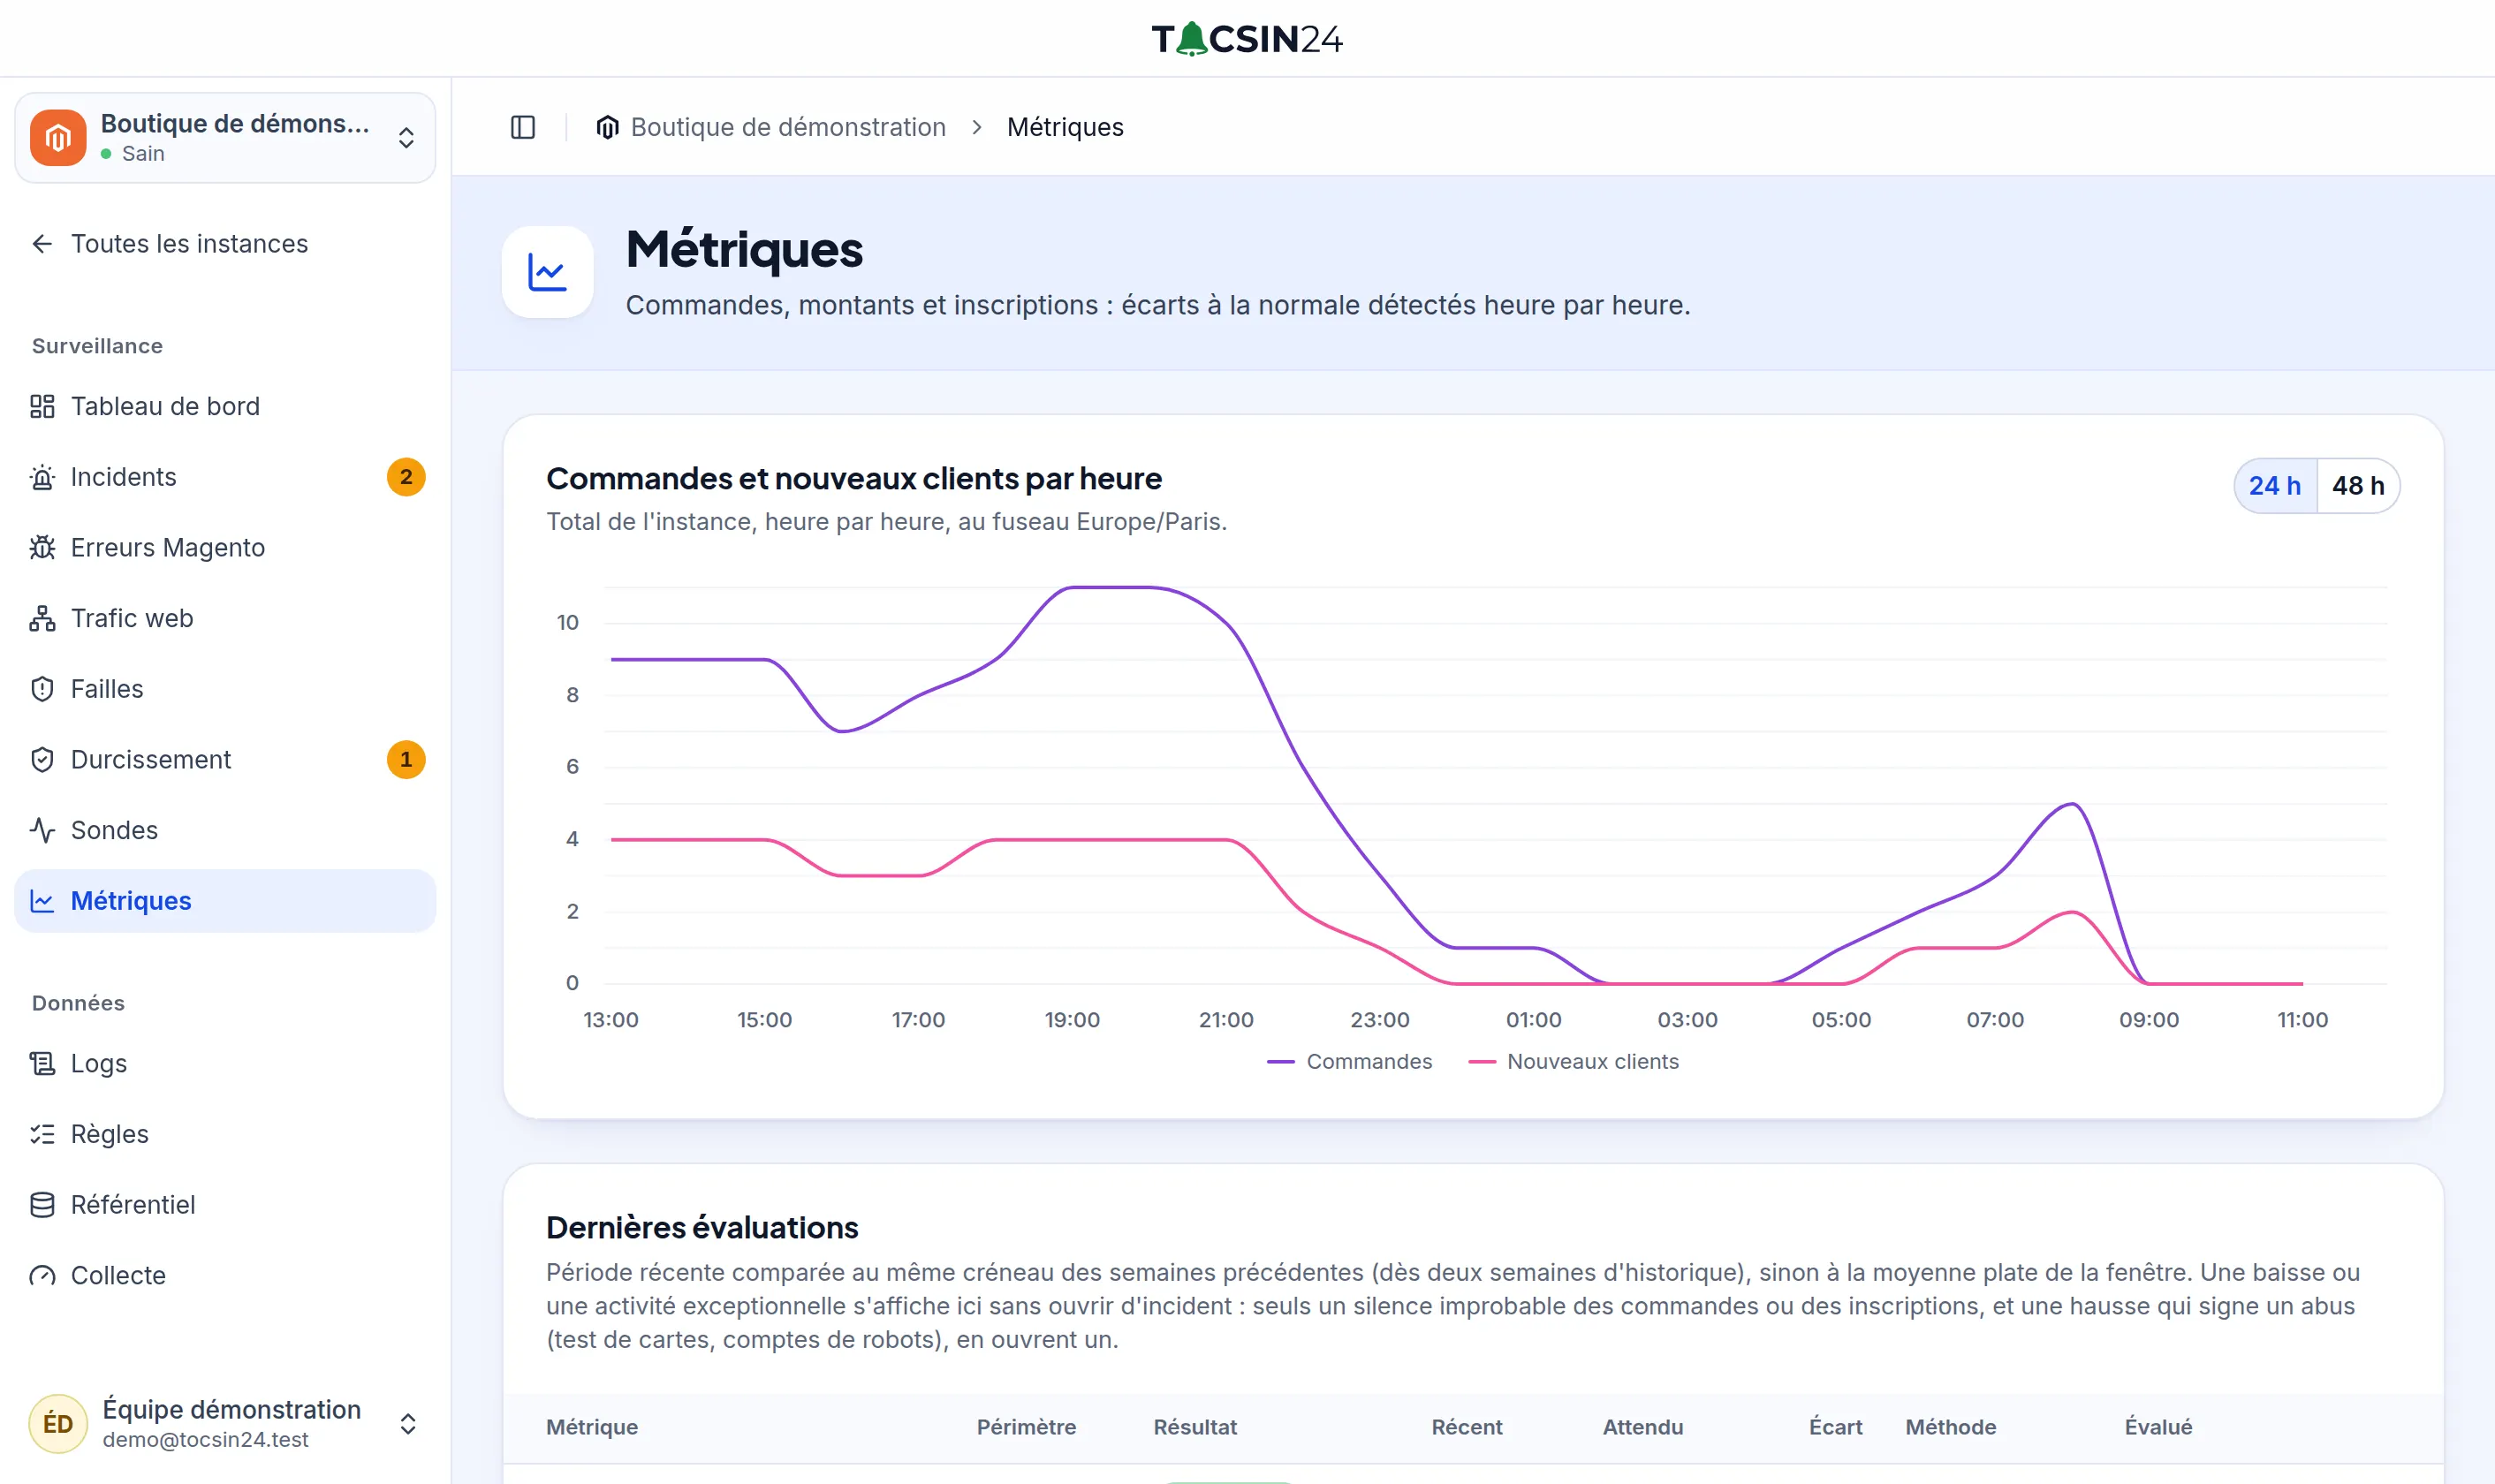
Sales
Orders, revenue and sign-ups hour by hour, with unusual dips reported.
Installed with Composer
Read-only, for Magento Open Source and Adobe Commerce 2.4.4 to 2.4.9.
€49 excl. VAT per month, per store or €490 excl. VAT per year
- Staging sites at half price
- Assisted setup from €290 excl. VAT
Questions
My hosting provider already applies the patches: why do I need Tocsin24?
To check that they really are applied, on your store, and to warn you the day a security bulletin comes out and has not been applied.
Does the module work with Hyvä?
Yes. The module does not touch the storefront: it works the same way with Hyvä, Luma or a custom theme.
Do you need SSH access?
No. The module is installed with Composer like any extension, and that is enough for monitoring. To also analyse the server and Magento logs, Tocsin24 needs SFTP access to the log files, ideally through a dedicated account limited to those folders. No command is ever run on the server.